27 separate products designed to remain coherent as one portfolio.
The portfolio is coherent because common record-governance principles, shared identifiers where needed and consistent reporting disciplines are applied across independent applications.
- 0
- Independently operable applications
- 0
- Layers that hold across all of them
- 0
- Named records that cross a boundary
- 0
- Applications relevant in more than one area
Five common architectural layers from governed record upward
The portfolio is an architecture rather than only a catalogue because common governance layers apply consistently while application data and responsibilities remain independent.
- Layer 1
The record
Each application governs a defined class of industrial record end to end and does not require another Zemerc application to own that record on its behalf.
Defined ownership for each governed record class - Layer 2
The rules on it
Common control patterns such as immutability, effective dating, supersession and segregation of duties are applied consistently where relevant to the governed record.
Consistent controls wherever they apply - Layer 3
The shared registers
Shared master entities such as equipment, personnel, organisations and locations use consistent identifiers where cross-application reference is required.
Shared entities referenced consistently rather than duplicated unnecessarily - Layer 4
The crossings
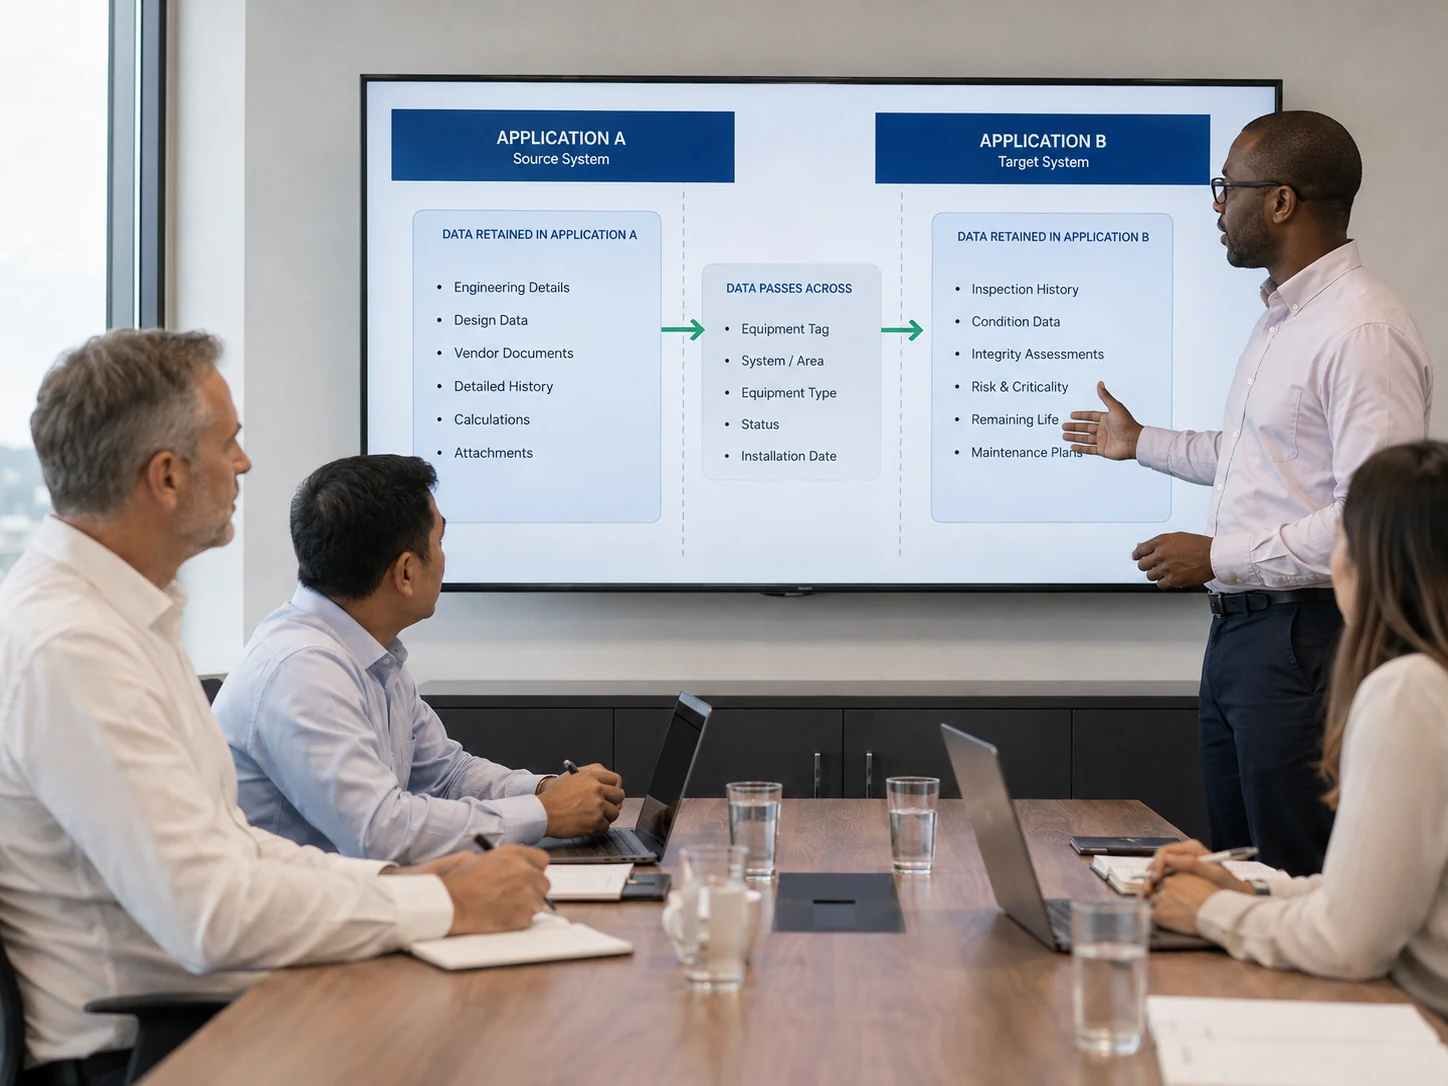
Where work passes between teams, exchanged records cross an explicit boundary while each application retains its own governed history.
A named governed record crossing an explicit boundary - Layer 5
The reporting language
Across the portfolio, derived figures state what is counted, what is excluded and when a result is unavailable. This provides a consistent reporting language without forcing every discipline into the same metric.
A consistent discipline for stating derived figures
One named record crossing one explicit boundary
Portfolio integration is based on explicit record boundaries rather than a mandatory shared data lake. When work passes between teams, the exchanged information remains named, governed and traceable.
- PMSLGMS
Receipt: a received item can trigger the logistics activity required to move it
- LGMSCCMS
Delivered item: receipt and acceptance records support installation and testing readiness
- CCMSSPIR
Completed system: verified completion evidence becomes part of the handover record
- QMSCCMS
Inspection and test record: quality evidence can become completion evidence
- IFMSPDMS
Open interface: an unresolved boundary can become a delivery exposure
- TSMPSM
Safety-critical element: a design definition becomes an operational assurance obligation
- PSMAIRMS
Barrier assurance: an assurance obligation can become an inspection or integrity activity
- AIRMSEAMS
Defect: an integrity finding can generate maintenance work with a verification step
- EAMSRAMS
Failure event: maintenance history can provide evidence for reliability analysis
- RAMSOMS
Critical-item exposure: a reliability driver can become a supportability concern
- FAMSHAMS
Production network: governed engineering context can support measured and allocated production records
- HAMSESG
Measured production: governed operating data can support sustainability disclosure
- HSERMS
Incident record: operational safety evidence can inform enterprise-risk assessment
- HSELLMS
Investigation finding: governed learning can become reusable organisational knowledge
Four things the portfolio deliberately does not require
Architectural trust also depends on deliberate exclusions. These boundaries preserve genuine application independence.
No shared database
Applications do not depend on direct reads of another product’s database tables. Where information crosses a boundary, it does so through an explicit governed record or interface, while each application retains its own history.
No portfolio-wide status field
There is no single portfolio-wide health score combining all operating areas. Each discipline reports using its own supportable measures.
No mandatory order of adoption
There is no mandatory first application. Any Zemerc application can be adopted independently where it meets the client’s requirement.
No hidden dependency
Where applications are useful together, the relationship is stated explicitly. No application is designed to fail or lose core capability when another Zemerc product is absent.
One operating philosophy with explicit cross-product relevance
Every application has one primary operating area. 12 are also relevant to another operating area, and those relationships are recorded explicitly in the portfolio architecture.
- Also relevant:EDMS
Shared entities remain consistently identified wherever referenced
Shared reference data matters because cross-application interpretation depends on consistent identification of entities such as equipment, personnel, organisations and locations.
- Shared entities use consistent identifiers wherever referenced
- A crossing transfers a named governed record while each application retains its own history
- Derived figures follow a consistent reporting discipline across operating areas
Two other ways to explore the portfolio
This page explains the architecture. Use the application directory or reference index when the immediate goal is product selection.
Bring two systems whose records need to align.
The important architectural question is the boundary: what information crosses between applications, what remains separate and why.