Technical and professional services around independently operable applications.
Zemerc supplies applications for your teams to operate, and provides the implementation, configuration, migration and deployment work around them. Every application runs without any of it; services are available where you want the work done with you, or done for you.
Three ways to work with Zemerc.
The engagement model is a commercial choice and does not change the application's core product architecture.
- Option 01
Use our applications
Licence the application required and operate it with your own team. No additional Zemerc application or service is mandatory.
View the applications - Option 02
Work with Zemerc
Implementation, configuration, data migration and deployment support delivered with the team responsible for the governed record.
What Zemerc provides - Option 03
Deliver an agreed outcome
Where suitable, Zemerc can combine applications with specialist engineering or professional services to deliver a separately agreed outcome.
Discuss a requirement
Services are optional and are not a condition of application use. Find an application purchased on its own is a complete, independently operable application, and remains one whether or not Zemerc does any of the work around it.
4 service areas, each with a defined boundary.
These activities require client decisions as well as Zemerc delivery work. Client ownership of rules, approvals and operating choices remains substantive.
Implementation
Run the six-phase implementation sequence with the team that owns the record.
- Work through scope, structure, rules, migration and initial live operation with the record owner and approver
- Configure the application against client structures and working practices rather than imposing a generic hierarchy
- Compare derived positions with supporting operational evidence and investigate discrepancies at record level
- Identify the governed record and the team accountable for it
- Define who may change records, what makes them valid and who may approve them
- Confirm whether derived figures are supportable and acceptable to the responsible business or technical owner
Configuration
Translate client rules into controls enforced by the application
- Establish the hierarchy that supports the governed registers down to the level where work is performed
- Establish consistent master records for shared entities such as equipment, personnel, organisations and locations where required
- Configure roles, organisation scope, approval routes, segregation of duties and applicable template revisions
- Client-owned rules include approval authorities, validity criteria and retention expectations
- Confirm that the hierarchy reflects the client’s actual operating structure
- Identify configuration that must be locked after approval
Data migration
Migrate historical records while preserving provenance.
- Use governed data-management tools, templates and previewed imports to migrate historical records with controlled provenance
- Mark migrated records so historical provenance remains explicit
- Establish the agreed point from which the application becomes authoritative for its governed record
- Decide which historical records will migrate and which will remain in the existing system of record
- Confirm the cut-over date
- Migration does not create missing history. Where supporting records do not exist, the application preserves that limitation rather than manufacturing completeness.
Deployment
Establish the approved operating environment for the application
- Confirm the deployment modes supported by the selected application and configure the agreed option
- Configure identity and organisation scope because later access controls depend on them
- Hand over application sign-in and access arrangements appropriate to the agreed deployment model
- Select the supported deployment mode for the application, including customer-managed cloud or private-network deployment where available
- Client network, identity and infrastructure decisions
- Define availability and continuity requirements for inclusion in the relevant application agreement
Implementation decisions come from the people who own and govern the record.
Implementation establishes the client's own record-governance rules, including ownership, validity, approval and correction. The application enforces the agreed rules rather than inventing them.
- Implementation is built around the accountable record owner and authorised approver
- The implementation hierarchy must reflect the client’s operating structure before dependent configuration proceeds
- Derived figures are accepted only when the responsible team is prepared to rely on and defend them
Five decision points that shape an engagement.
Each decision point must have a supportable answer before implementation proceeds.
- 01
A working session
Bring a register, project, asset or vessel. The relevant application can be demonstrated against representative records with the people responsible for owning and approving them.
- 02
The scoping questions
Scope starts with the governed record, systems that remain in place, required end-state evidence and accountable stakeholders. Those answers determine whether and how an engagement should proceed.
- 03
Deployment and commercial terms
Deployment mode, availability, continuity and support arrangements are agreed for the selected application and documented in the applicable commercial agreement.
- 04
The first live period
Applications are tested on representative operational work with office and field users where relevant, and derived positions are checked against supporting records.
- 05
What follows depends on the agreed requirement
A client may adopt another application later if a separate requirement justifies it. No existing application depends on that decision.
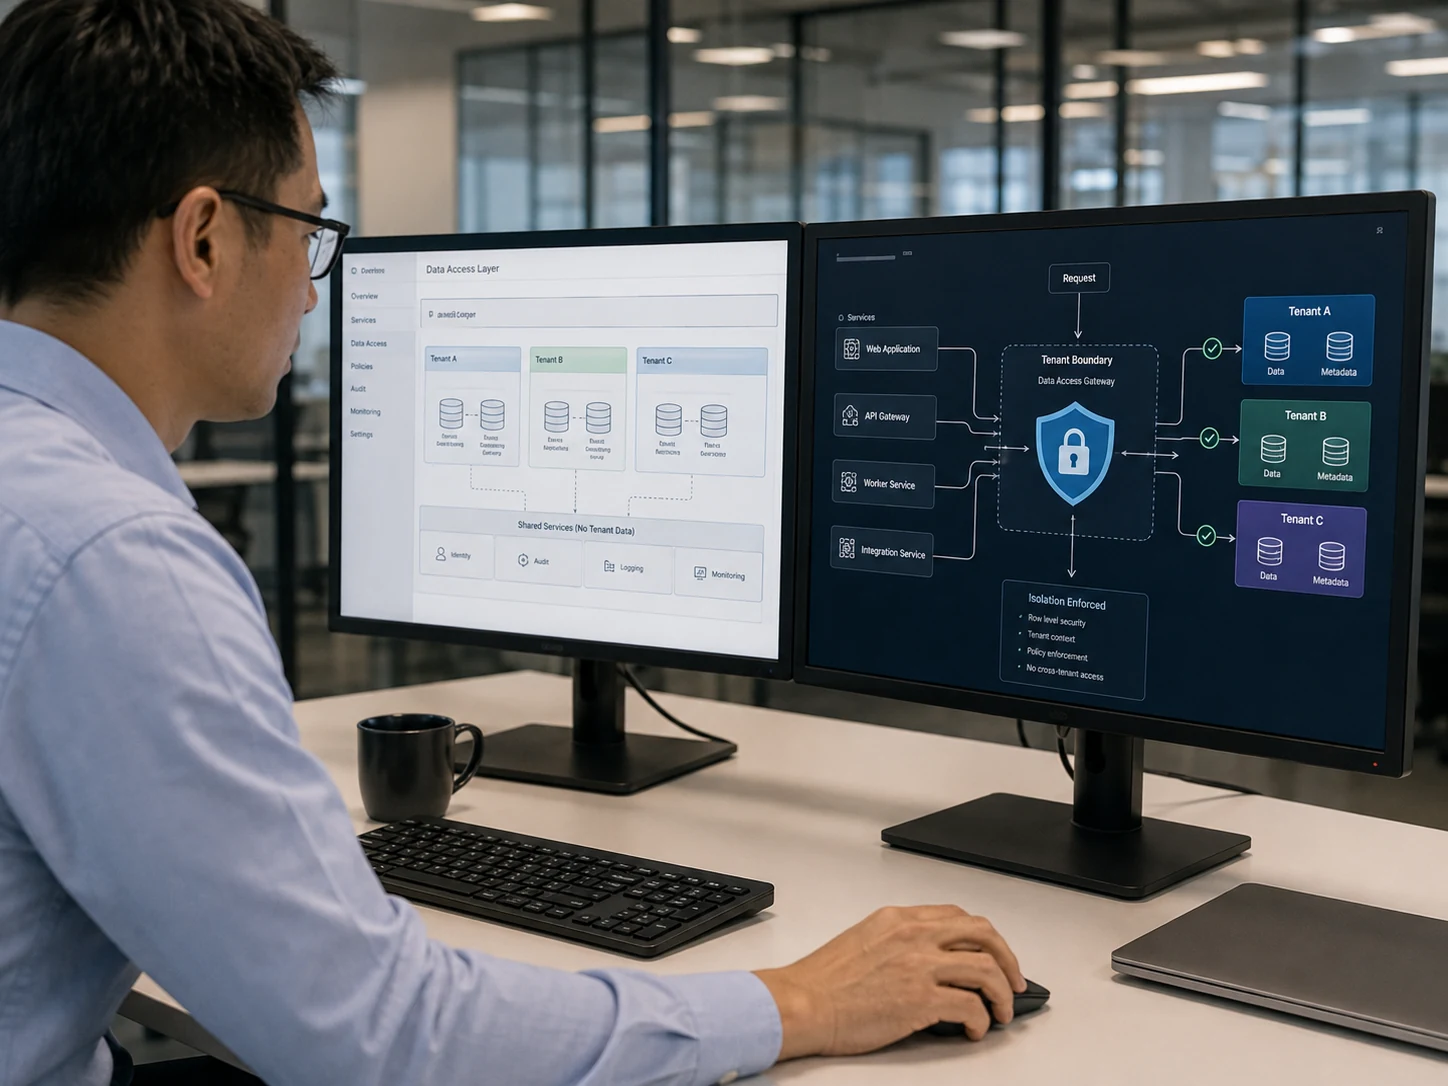
Deployment is agreed separately for each application.
Supported deployment modes vary by application and may include Zemerc-hosted, customer-managed cloud, private-network or offline operation where specifically supported. Availability is confirmed per product.
- Organisation data separation is enforced at the data layer as well as through application controls
- Roles, organisation scope and approval rights are enforced against authorised identities
- Each application has its own authentication boundary; no shared public application portal is currently provided
Four things this services page does not offer.
This page states both what Zemerc provides and what is not currently offered. Unestablished services are not presented as available.
Unscoped integration projects
Where integration catalogues exist, they do not represent tested live connections by default. Governed import and export provide controlled data movement, while external integrations are scoped, configured and tested separately.
Custom software forks
Applications are configured rather than customer-forked so clients remain on the supported product line.
Replacing effective incumbent systems without a defined need
Each application governs a defined class of record. Existing systems that already meet another requirement can remain in place.
Generic published service levels
Availability, support and response commitments are agreed for the specific application and deployment rather than stated generically on this page.
Applications remain products, not consulting engagements.
All 27 applications are independently operable and commercially standalone. Services on this page are optional and do not alter that architecture.
Services are not a licence condition
Applications remain independently operable products. Services exist to support adoption and delivery, not because the software requires consulting to function.
Services do not create product dependencies
Using Zemerc services does not create a dependency on another Zemerc application or a specific hosting model.
The governed record remains yours
The client retains ownership of data, approval authorities and validity rules. Zemerc configures the application to enforce those agreed decisions.
Start with the governed record, not the service package.
Bring one register, project or asset to a working session. The required implementation scope follows from the record, controls and operating context.